Hands-on with Azure Firewall: Hub-and-Spoke Architecture Deployment
Deploy Azure Firewall in a hub-and-spoke topology and force all VM traffic through it, then debug why network rules alone can't filter HTTPS and fix it with application rules.
Adds to your resume: Deployed Azure Firewall in a hub-and-spoke network, forced all spoke VM traffic through it, and fixed HTTPS filtering by replacing network rules with application rules.
Securing an Azure Virtual Network is often handled with Network Security Groups alone IP and port-level rules attached per NIC or subnet. That works for basic segmentation, but it breaks down once an organization needs centralized, Layer 7-aware control over what leaves its network: FQDN-based filtering, threat intelligence, TLS inspection, or a single place to see and manage outbound policy across many spokes.
NSGs are stateless and scoped per resource. They can't inspect HTTPS traffic by destination domain, can't apply threat intelligence, and don't give a security team one pane of glass across a hub-and-spoke estate.
The core question
How do you centralize outbound and inter-subnet traffic inspection for an Azure network with Layer 7 FQDN filtering, logging, and a single enforcement point without relying on per-resource NSG rules that don't scale and can't see application-layer traffic?
Azure Firewall vs. Network Security Groups
| Aspect | Azure Firewall | Network Security Groups |
|---|---|---|
| OSI Layer | Layer 3–7 (stateful) | Layer 3–4 (stateless) |
| Scope | Protects entire subnets/networks | Protects individual NICs/subnets |
| State management | Maintains connection state | No state tracking |
| FQDN filtering | Full FQDN support with SNI | IP-based only |
| Threat intelligence | Built-in malware/botnet detection | None |
| Centralized management | Single pane via Firewall Manager | Individual rule management |
| Performance overhead | Single firewall instance for all traffic | Distributed, lower latency |
| Cost model | Pay for throughput | Pay per rule |
| Use case | Organization-wide security policy | Granular VM-level access control |
Key rule: NSG rules are evaluated after Azure Firewall. If Azure Firewall allows traffic but the NSG blocks it, the traffic is blocked both layers must permit it for traffic to pass.
Internet → Azure Firewall → NSG → Virtual MachineIf traffic is blocked at any layer, it terminates there.
Architecture this use case builds
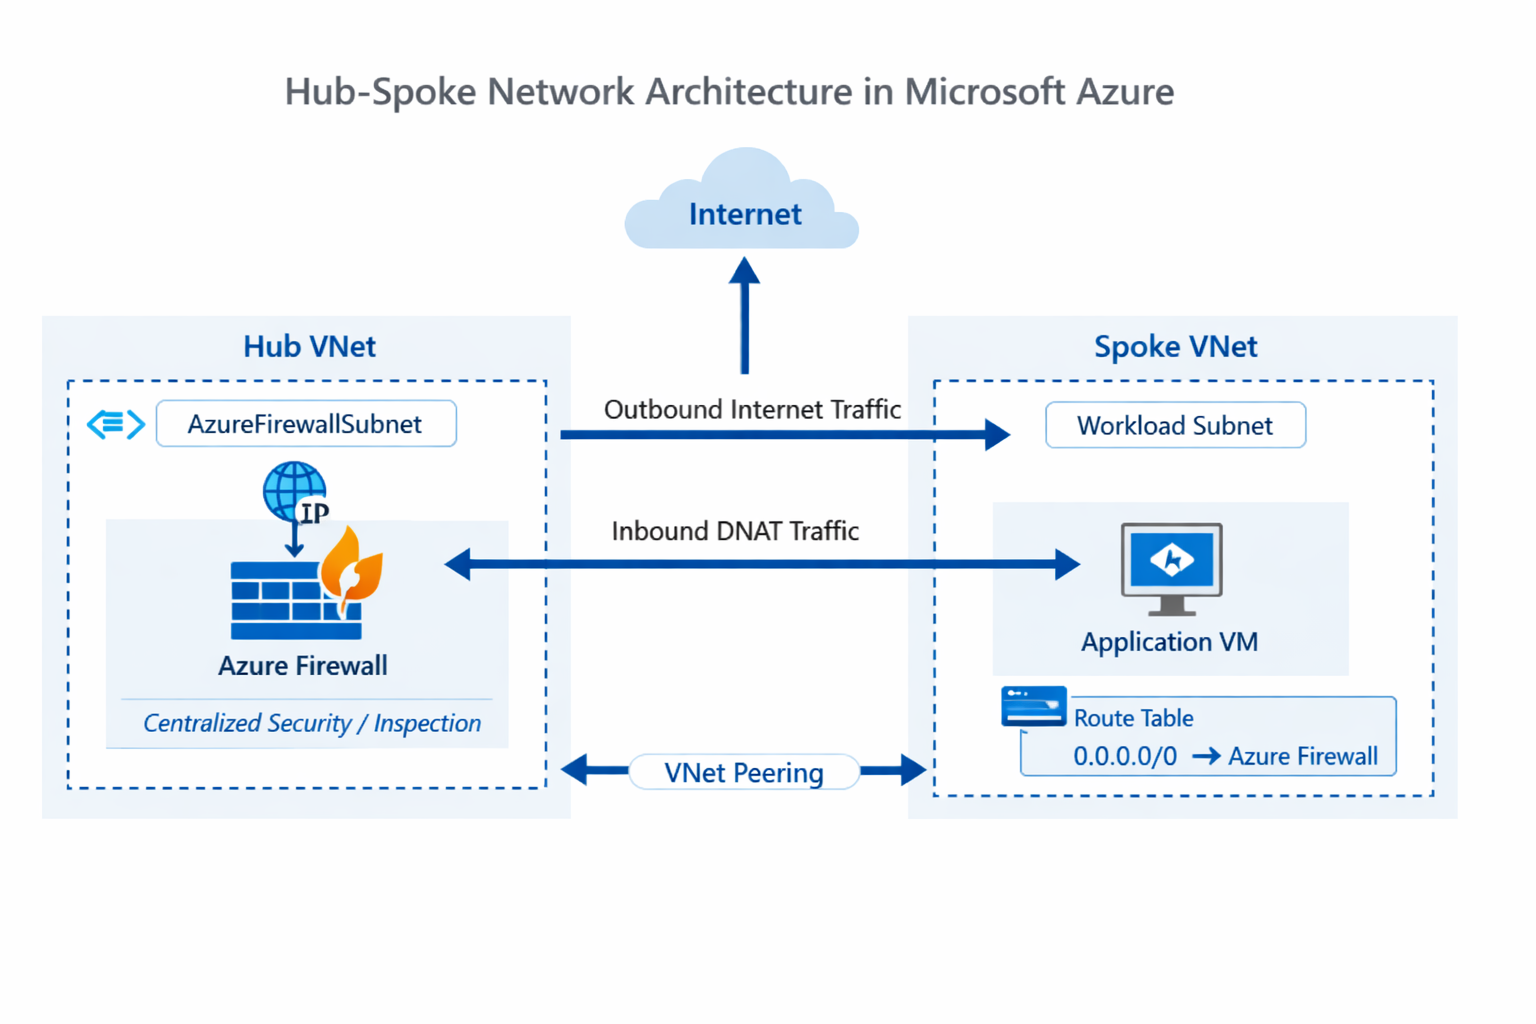
- A separate VNet for the firewall (Hub)
- A separate VNet for application resources (Spoke)
- Azure Firewall, centralizing inspection between them
- A virtual machine in the spoke, as the workload being protected
What this gains you
- One enforcement point for outbound and inter-subnet traffic, instead of per-resource NSG rules
- Layer 7 visibility: filtering by FQDN, not just IP and port
- Built-in threat intelligence (and, on Premium, TLS inspection and IDPS)
- A routing pattern hub-and-spoke with user-defined routes that scales to many spokes behind one firewall
Choosing a SKU
Azure Firewall Basic - small-to-medium businesses, non-mission-critical workloads
- Throughput up to 250 Mbps, unlimited concurrent connections, availability zones supported
- L3–L7 stateful filtering, FQDN-based application rules, network rules with service tags, SNAT/DNAT, basic (alert-only) threat intelligence, full logging
- Best for testing, development, and modest-traffic production workloads
Azure Firewall Standard - enterprise organizations, mission-critical workloads
- Throughput up to 30 Gbps, 1 Gbps per flow, automatic autoscaling
- Adds web categories, DNS proxy, active-blocking threat intelligence, 100+ service tags, FQDN tags, a policy analytics dashboard, multiple rule collection groups, outbound traffic control
- Best for most enterprise deployments needing robust threat protection
Azure Firewall Premium - highly regulated industries, sensitive data
- Throughput up to 100 Gbps, 10 Gbps per flow
- Adds TLS/SSL inspection, IDPS, full-path URL filtering, enhanced web categories with SSL termination, east-west TLS inspection, advanced malware detection
- Best for payment processors, healthcare, finance, and anyone handling regulated PII
Decision guide
- Throughput under 250 Mbps → Basic
- Throughput 250 Mbps–30 Gbps with standard threat protection needs → Standard
- Throughput over 30 Gbps, or TLS/HTTPS payload inspection required → Premium
Use this approach when
- You're moving from per-VM NSG rules to centralized, organization-wide traffic policy
- You need to filter or block outbound HTTPS by destination domain (FQDN), not just IP and port
- You're building or standardizing a hub-and-spoke network topology
- You need a single place to view traffic logs and threat intelligence across your Azure estate
- Compliance requires inspecting, not just routing, east-west or outbound traffic (Premium tier)
When this is not the right fit
- A single VM or small flat network where NSGs already cover the access control you need Azure Firewall adds cost and complexity that a one-resource setup doesn't need
- You need per-NIC or distributed, lowest-latency enforcement rather than a single centralized inspection point
- You don't yet have (or plan to adopt) a hub-and-spoke topology the routing patterns in this lab assume one
Accounts and access
- An Azure subscription with rights to create VNets, subnets, route tables, a public IP, Azure Firewall (Standard SKU), and a virtual machine
Lab objective
Design and implement a production-style hub-and-spoke network topology using:
- Azure Virtual Network
- Azure Firewall (Standard SKU)
- VNet peering
- User-defined routes (UDR)
- Traffic redirection through the firewall
This demonstrates controlled internet egress, centralized security inspection, and an enterprise routing pattern.
Design principles
- Centralized security
- Scalable hub-spoke model
- Route-based traffic control
- No direct internet access from the spoke
Before you start
- Decide your naming convention and CIDR ranges for the hub and spoke VNets up front
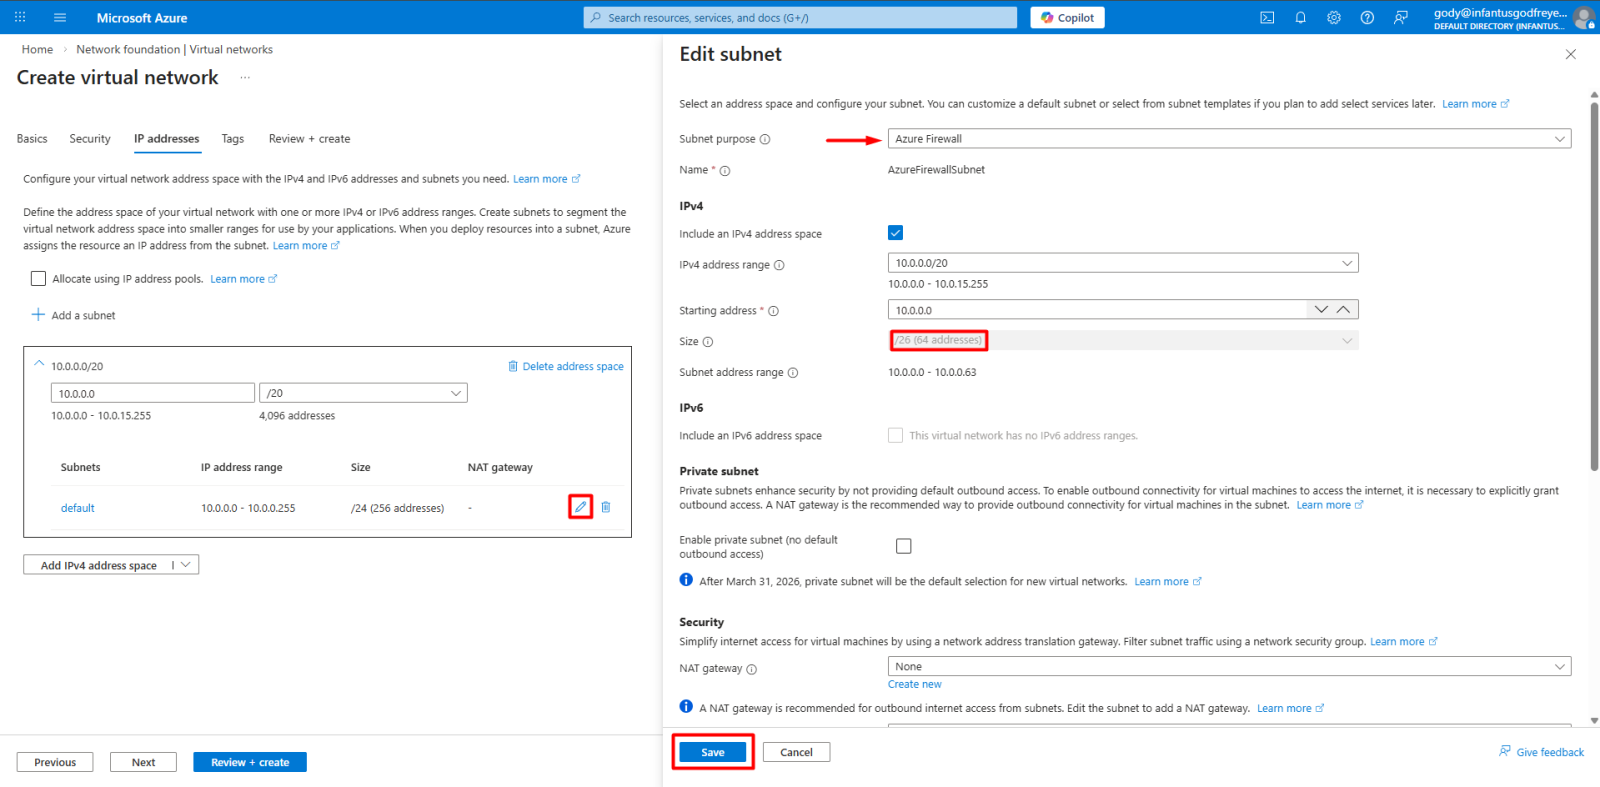
- The firewall subnet must be named exactly AzureFirewallSubnet, sized /26 or larger the portal will not let you proceed otherwise
- Have a plan for which ports the spoke VM's NSG needs open (this lab uses 22, 80, 443)
Architecture Overview
Step-by-Step Deployment Guide
Step 1: Create the hub virtual network (firewall VNet)
- Azure Portal → VNet
- Select your subscription
- Enter the resource group and VNet name
- Select the region
- Enter the CIDR block address
- Select subnet purpose AzureFirewallSubnet the subnet name auto-populates
- Set the subnet size to /26
- Click Save
Note:
The AzureFirewallSubnet is a private subnet inside the VNet.
It gets:
- Private IP(s)
- No public IP directly assigned
Public connectivity comes via:
- Public IP resource attached to Azure Firewall
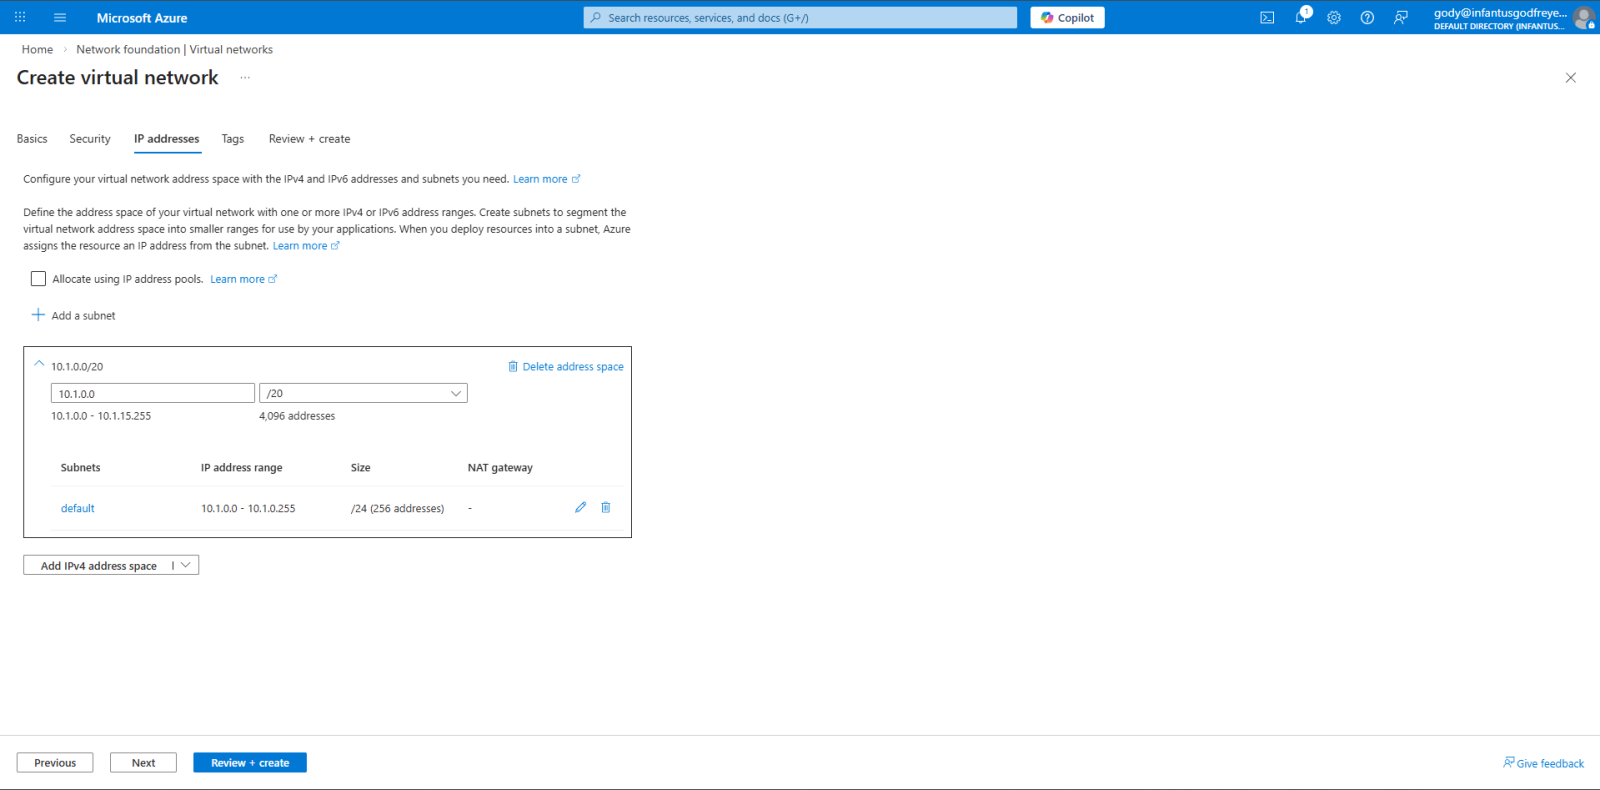
Step 2: Create the spoke virtual network (VM network)
- Azure Portal → VNet
- Select your subscription
- Enter the resource group and VNet name
- Select the region
- Enter the CIDR block address
- Enter the subnet size
- Click Save
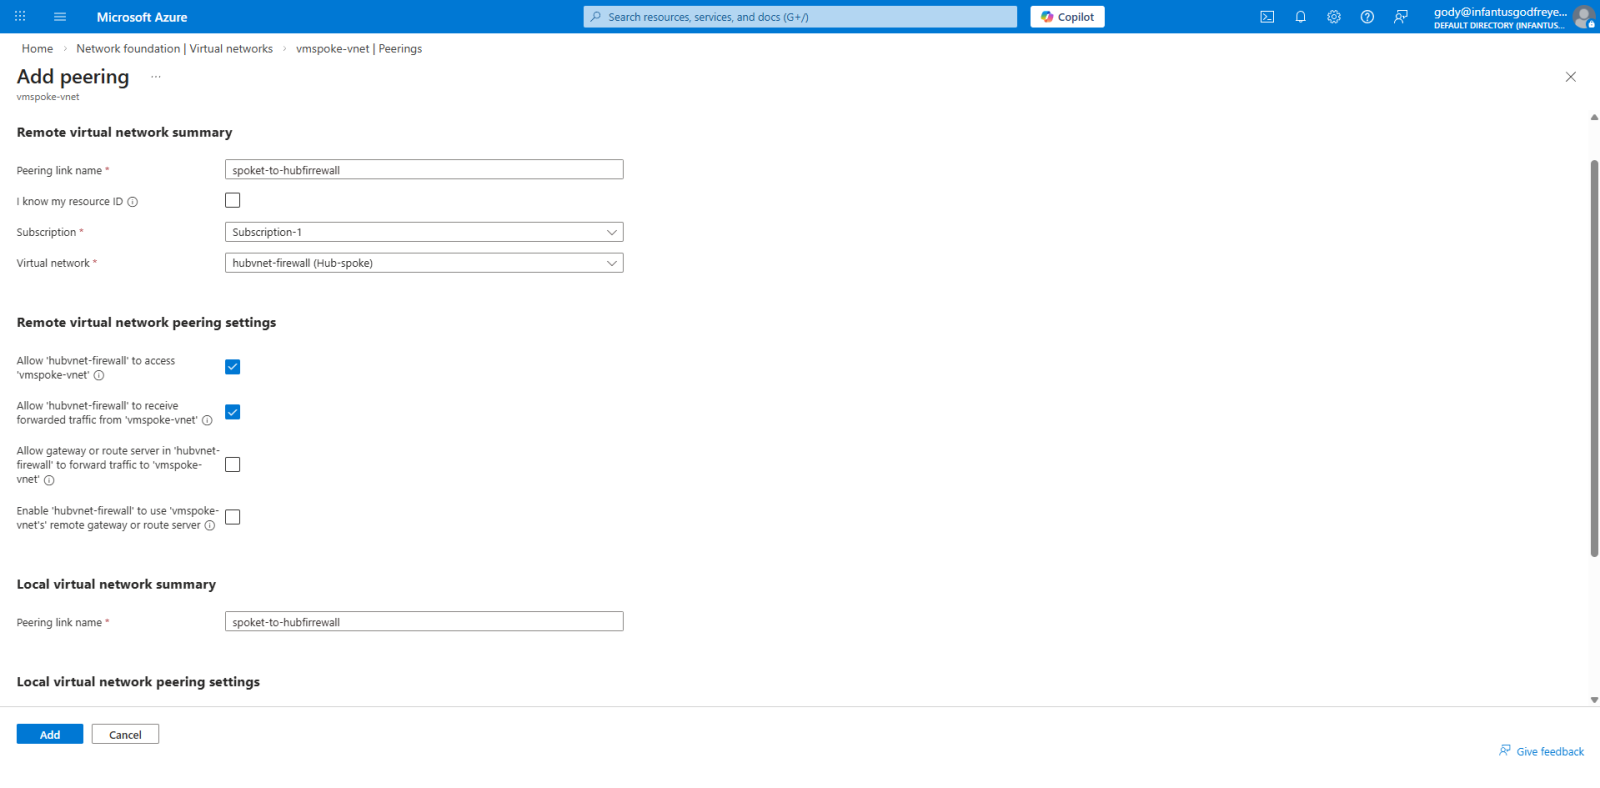
Step 3: Configure VNet peering (hub–spoke)
- Go to the spoke VNet and add peering with the hub VNet
- Enter the VNet peering name
- Select your subscription
- Select the target VNet to peer with (the hub VNet)
- Enable Allow hub-firewall to access spoke-VNet and, on the other side, Allow spoke-VNet to access hub-firewall
- Enable Allow hub-firewall to receive forwarded traffic and, on the other side, Allow spoke-VNet to receive forwarded traffic
Why “Allow Forwarded Traffic”?
Because Azure Firewall will act as a routing appliance.
Without this, traffic redirection will fail.
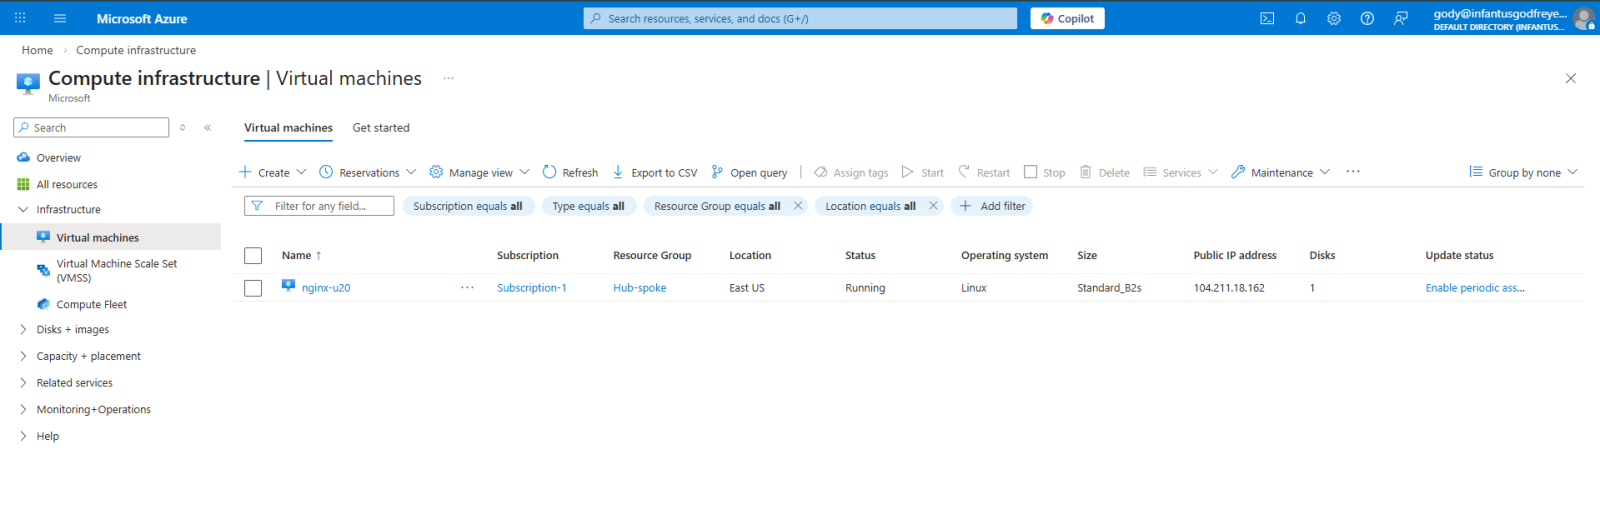
Step 4: Create a VM inside the spoke VNet
- Create a VM inside the spoke VNet with the required network security group, like 22,80,443 ports
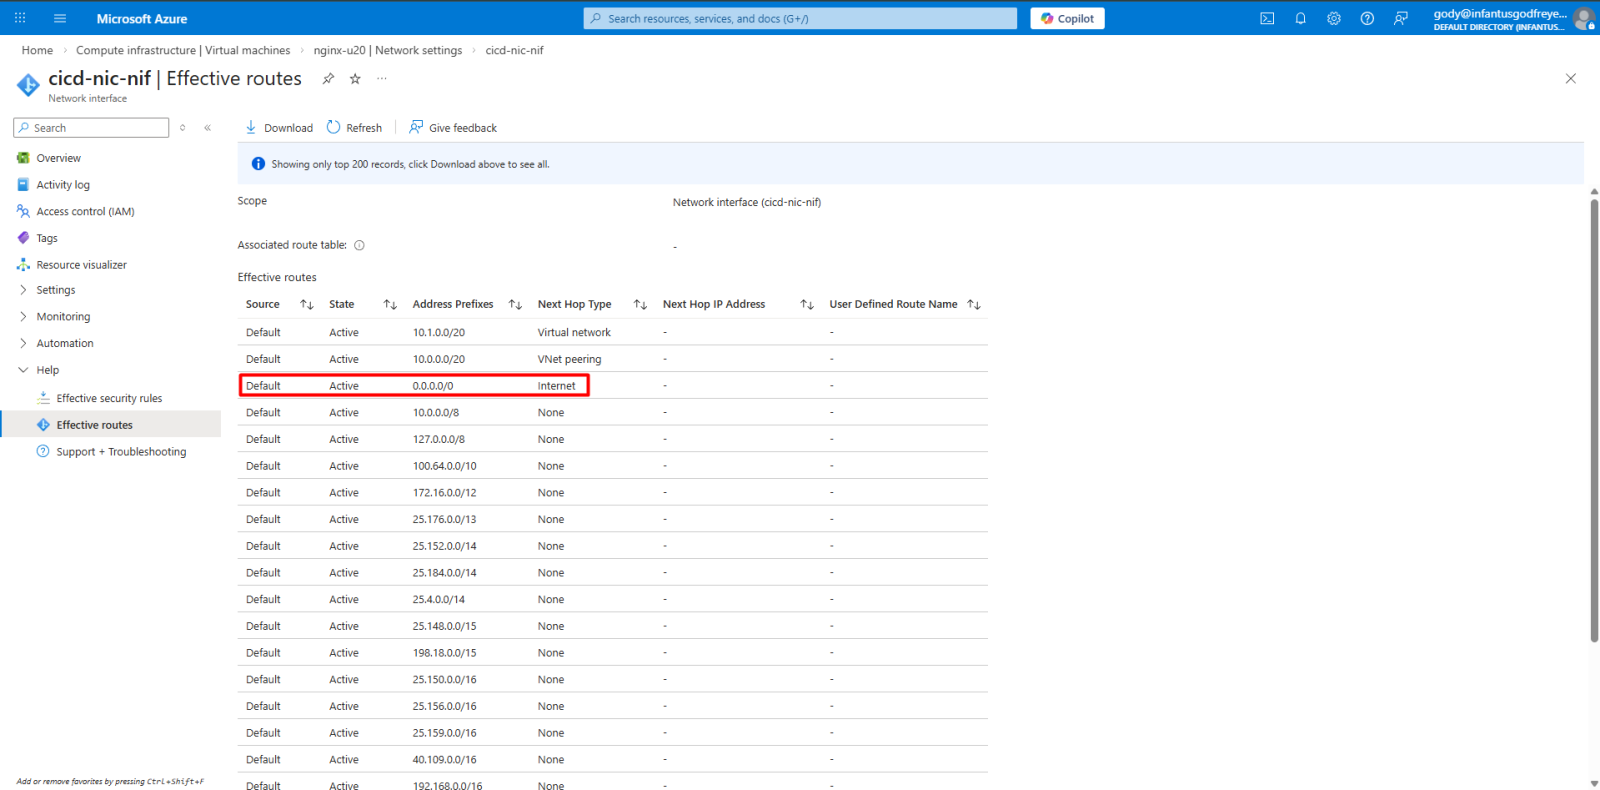
Step 5: Validate Default Routing (Before Firewall)
- Open the VM's NIC → Effective routes
At this point you'll see the VM has direct internet access to 0.0.0.0/0 Azure's default system route.
Step 6: Deploy Azure Firewall
Azure Portal → Firewall
| Setting | Value |
|---|---|
| Name | hubfirewall |
| Region | East US |
| Availability Zone | None |
| Firewall SKU | Standard |
| Firewall Management | Use Firewall Policy |
| Firewall Management | Add new Firewall Policy |
| Virtual Network | hubvnet-firewall |
| Public IP | Create new PIP for the firewall |
NOTE: Standard SKU is used for this lab.
Step 7: Create a route table (UDR)
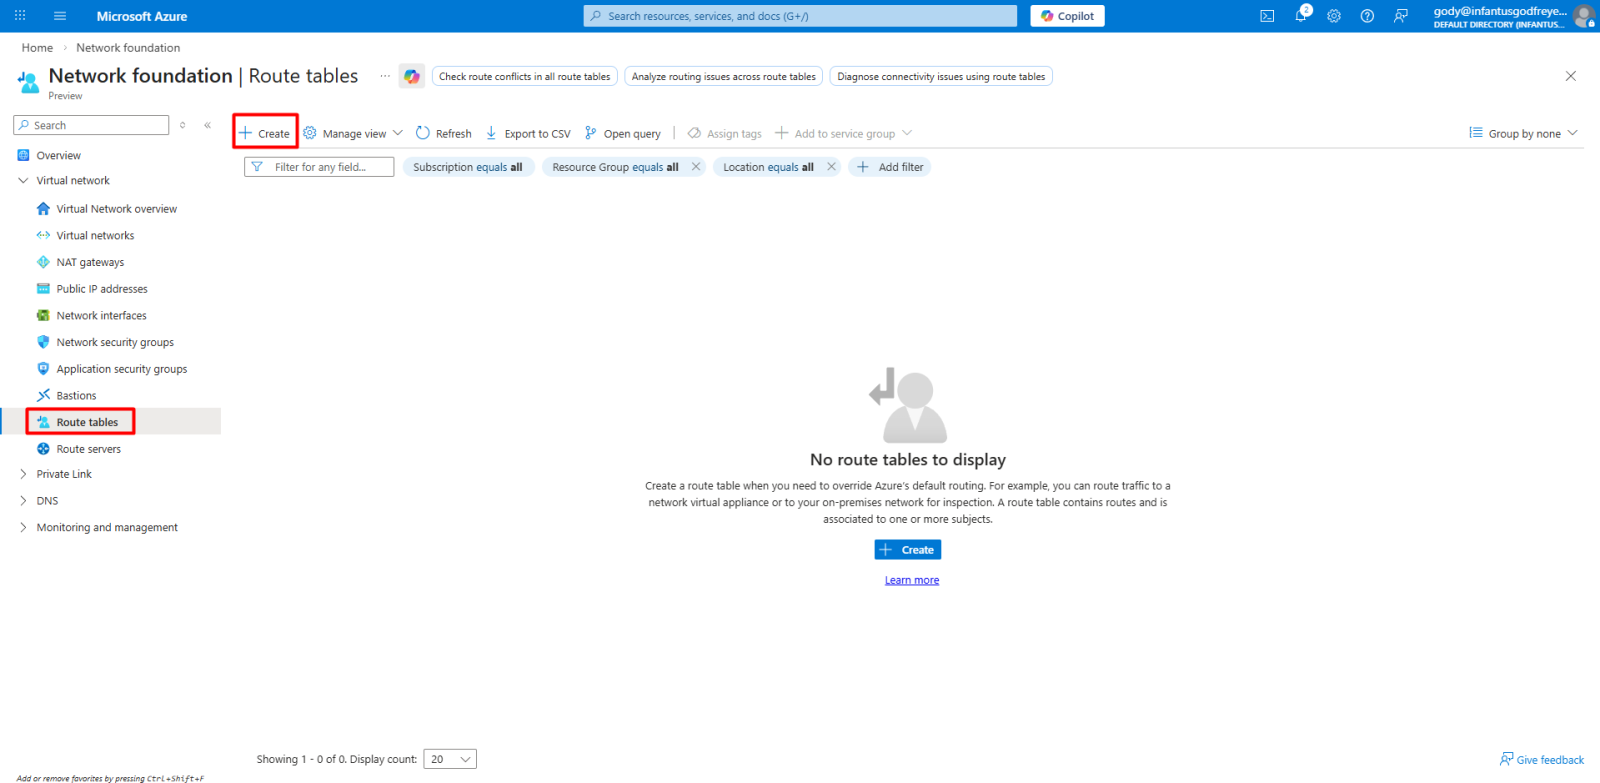
- Route Tables → Create
- Enter the subscription, resource group, name, and region
Step 8: Add a default route to the firewall
Go to routes on the created route table and add:
| Field | Value |
|---|---|
| Route Name | hubfw-route |
| Destination | 0.0.0.0/0 |
| Next Hop Type | Virtual Appliance |
| Next Hop Address | Firewall private IP |
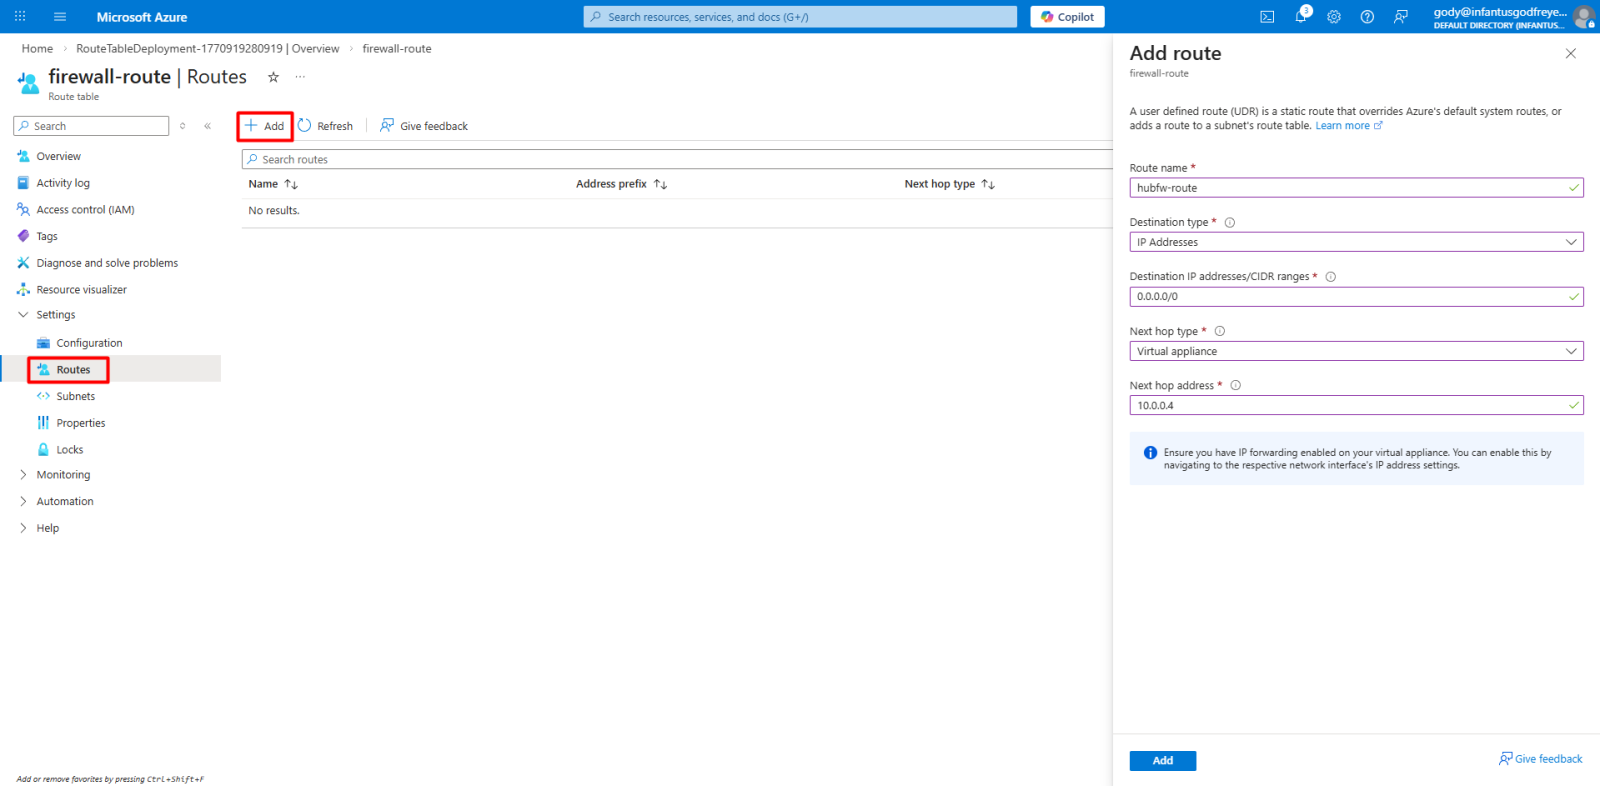
Where to find the firewall's private IP: Azure Firewall → Overview → Private IP address (e.g. 10.0.0.4). Use that as the next hop.
Step 9: Associate the route table with the spoke subnet
- Go to routes on the created route table and select subnets
- Associate the spoke VNet's VM subnet this is what forces its traffic through the firewall
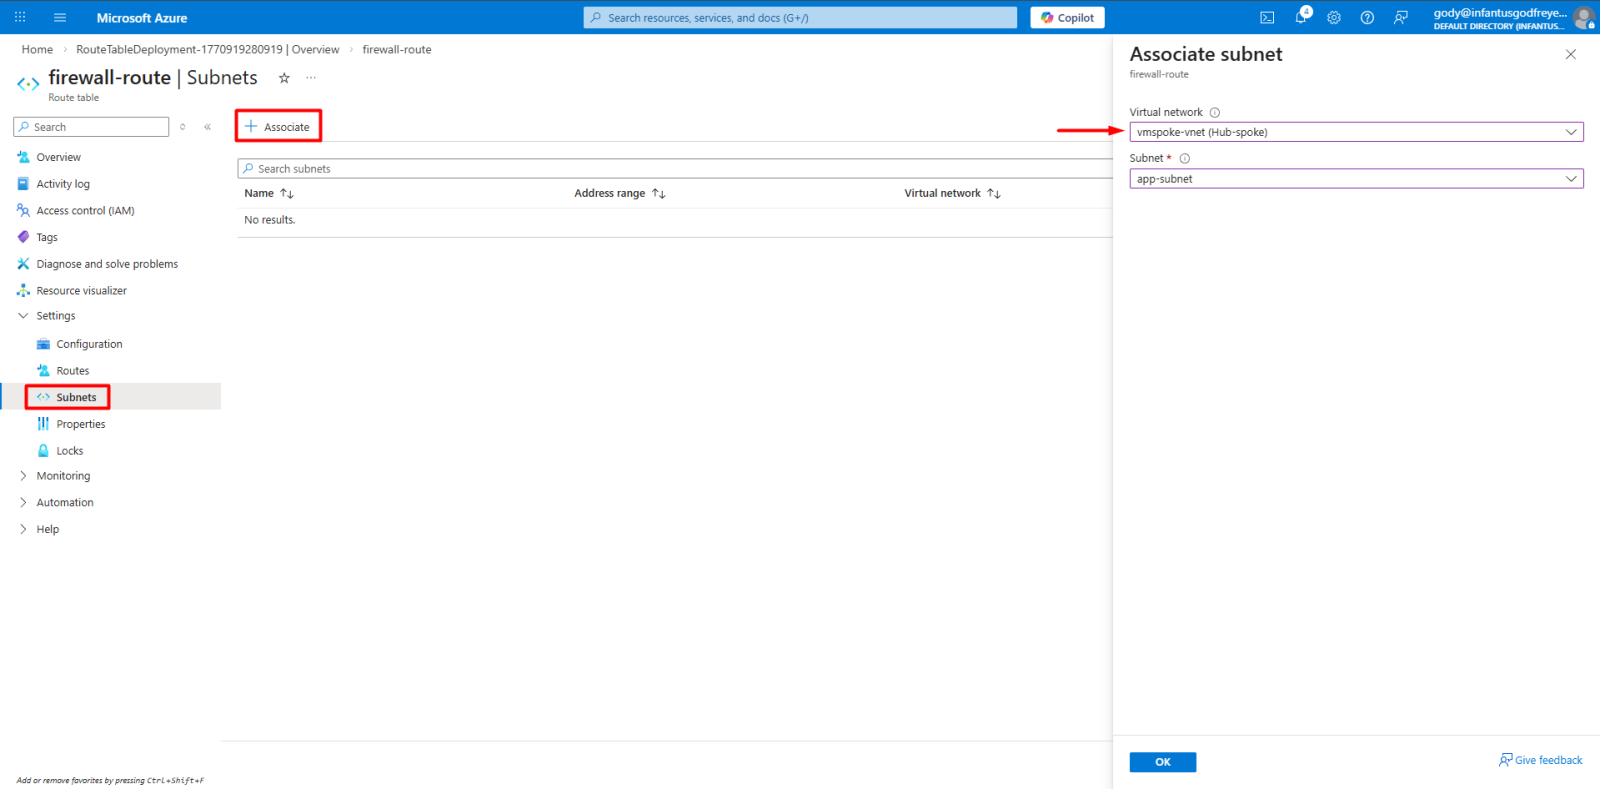
Step 10: Validate effective routes (after the UDR)
- VM → NIC → Effective Routes
You should now see 0.0.0.0/0 → Next Hop: Virtual Appliance (10.0.0.4), confirming traffic is forced through Azure Firewall.
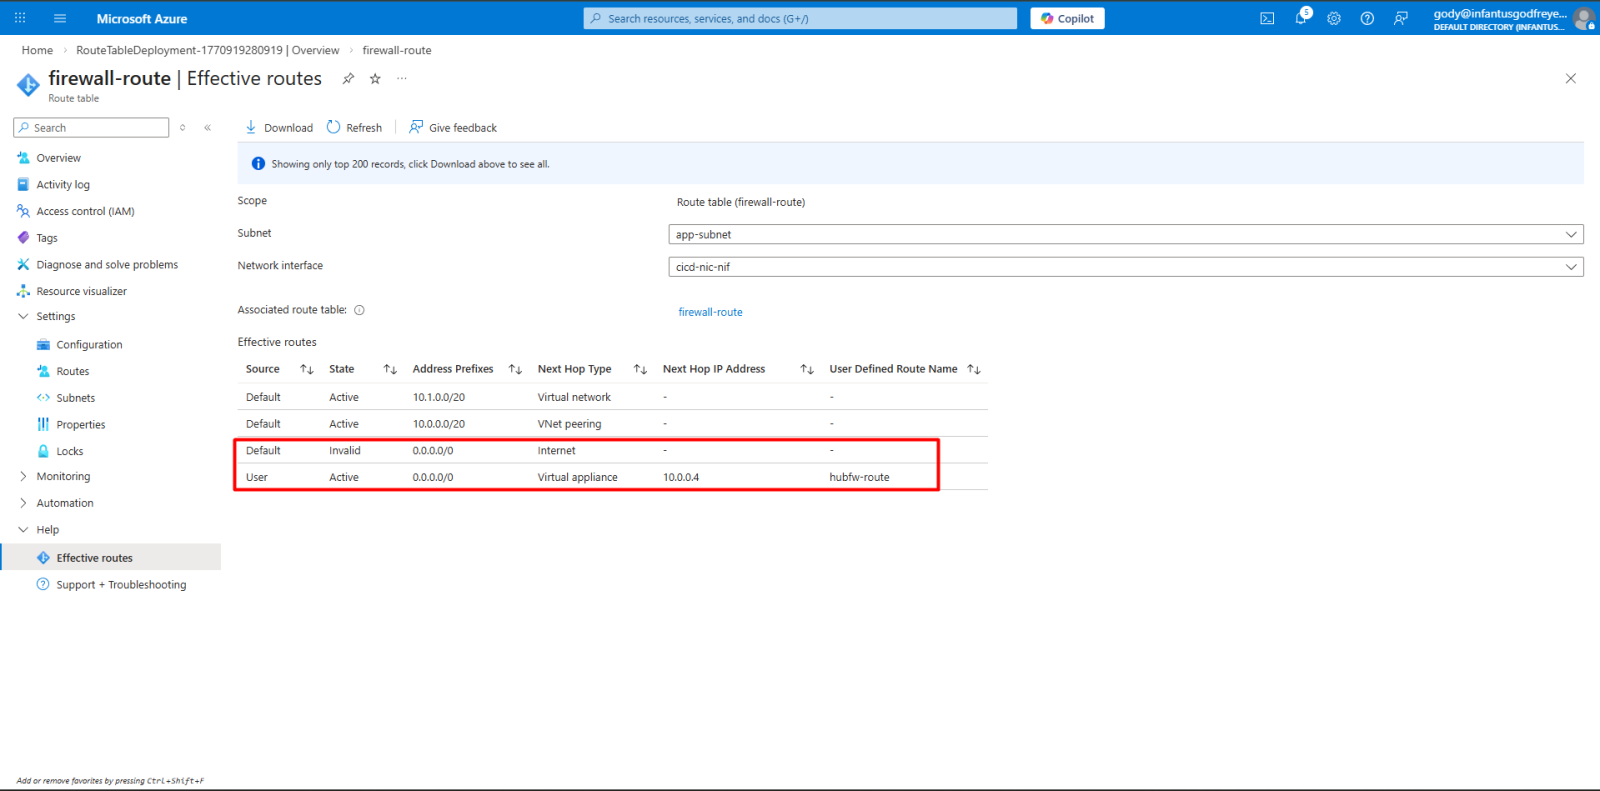
If this doesn't show, your route table isn't properly associated.
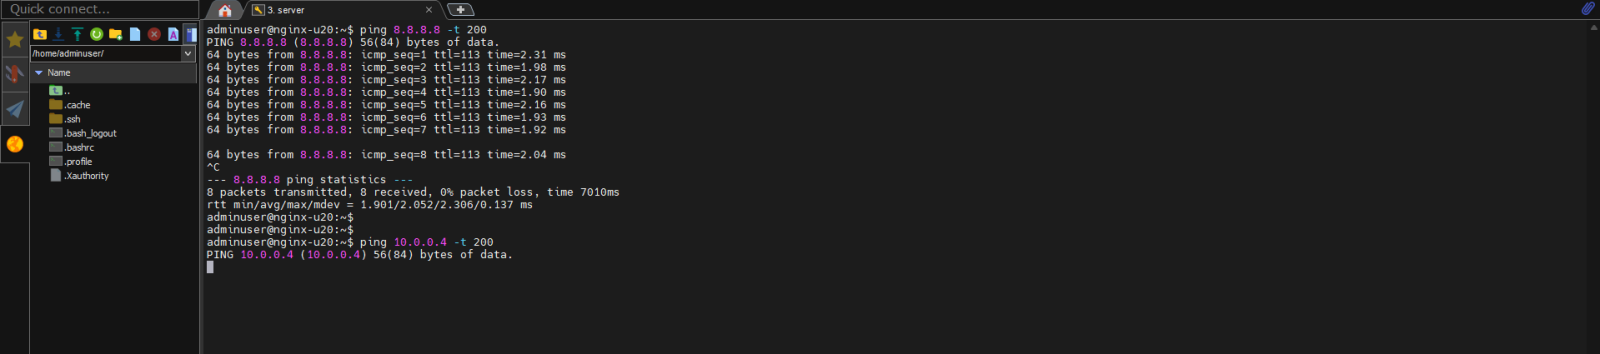
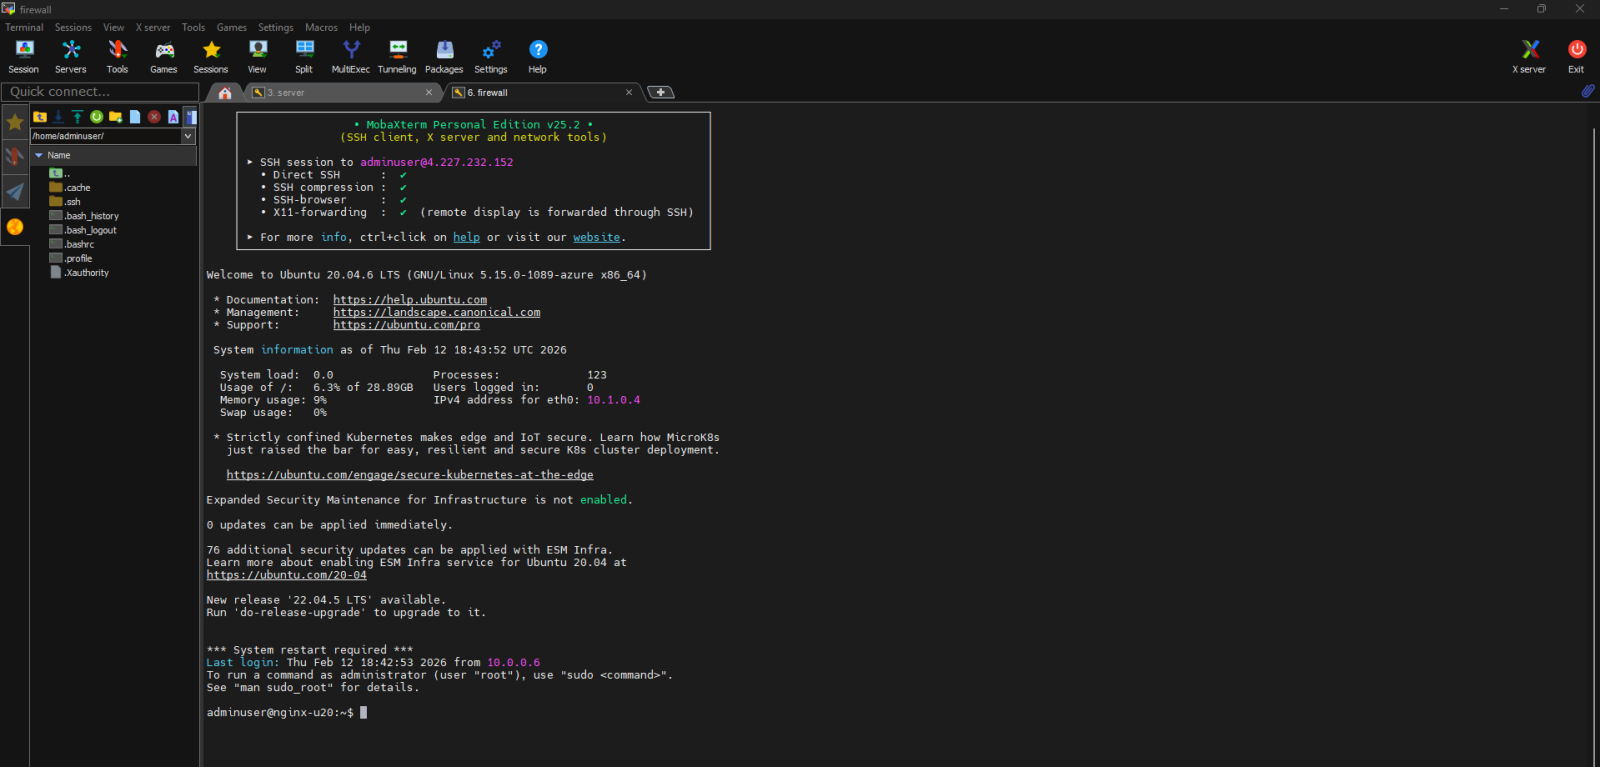
At this point, SSH to the VM stops working. Traffic now flows VM → Firewall → Internet, but no firewall rule exists yet. Azure Firewall's default behavior is deny all outbound, deny all inbound.
Step 11: Create a DNAT rule
A DNAT rule (Destination Network Address Translation) publishes an internal resource to the internet by translating a public IP/port to a private IP/port.
Azure Firewall → Firewall Policy → DNAT Rules:
| Field | Value |
|---|---|
| Rule Name | ssh-to-vm |
| Source Type | IP Address |
| Source | * (or restrict to your own public IP for production) |
| Destination Type | IP Address |
| Destination | Firewall public IP |
| Destination Port | 22 |
| Protocol | TCP |
| Translated Address | 10.1.1.4 (VM IP address) |
| Translated Port | 22 |
Once configured, you can SSH back into the VM but via the firewall's IP address.
Step 12: Create a network rule (Layer 3/4 control)
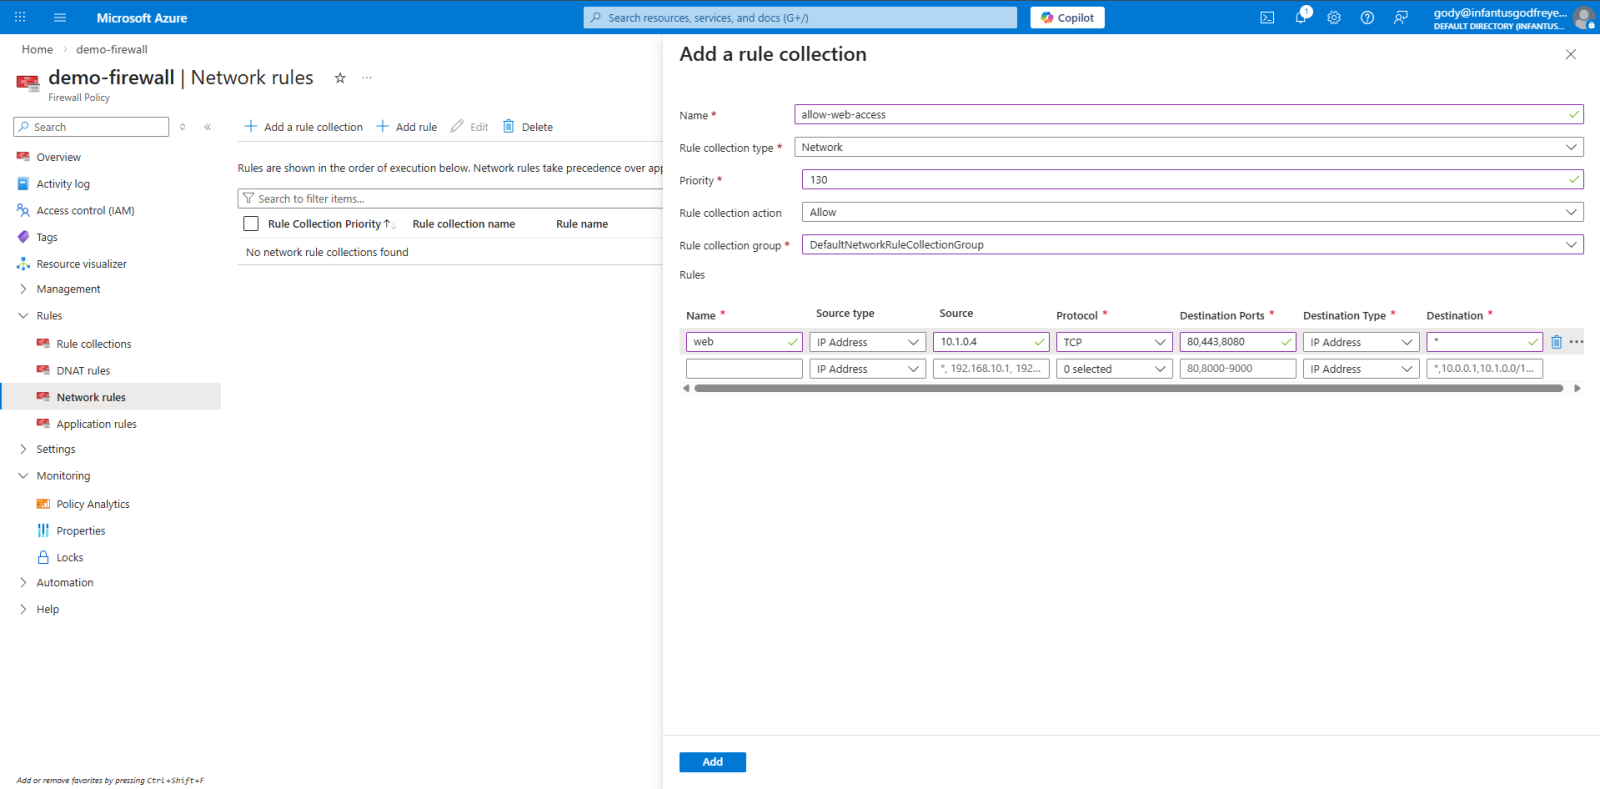
Firewall Policy → Network Rules → Add Rule Collection:
| Field | Value |
|---|---|
| Name | allow-web-access |
| Type | Network |
| Priority | 130 |
| Action | Allow |
| Source | 10.1.0.4 (VM private IP) |
| Protocol | TCP |
| Ports | 80, 443, 8080 |
| Destination | * |
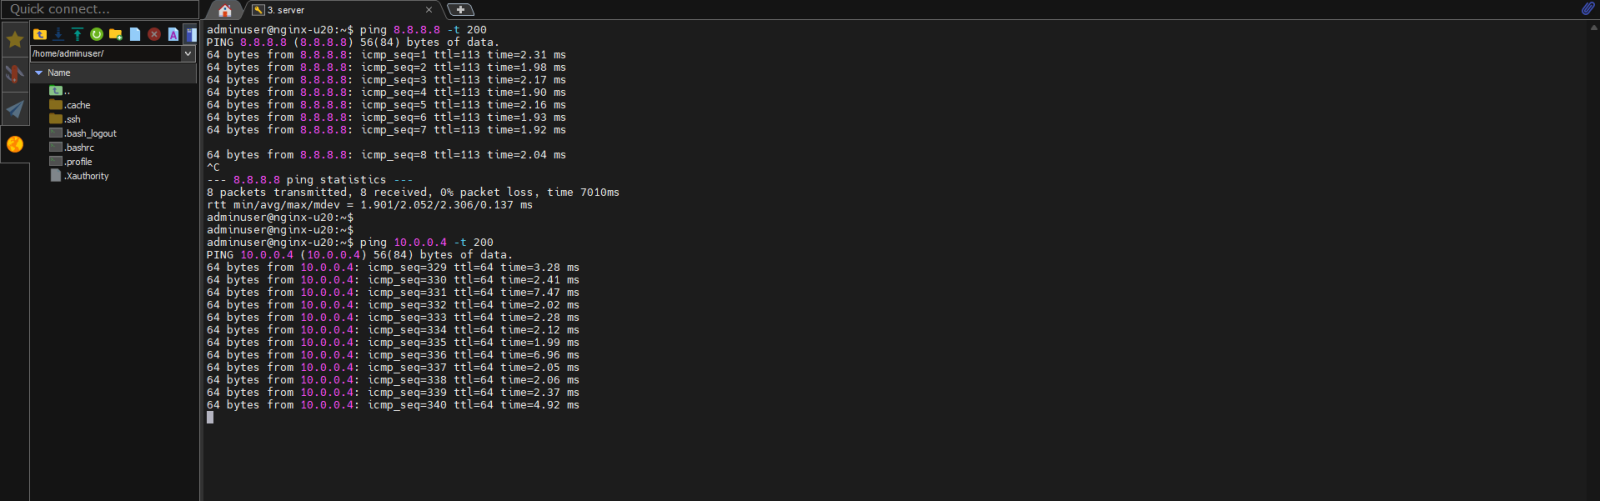
This allows raw TCP traffic. From the VM, ping 10.0.0.4 succeeds (firewall reachable), but curl https://www.google.com still fails.

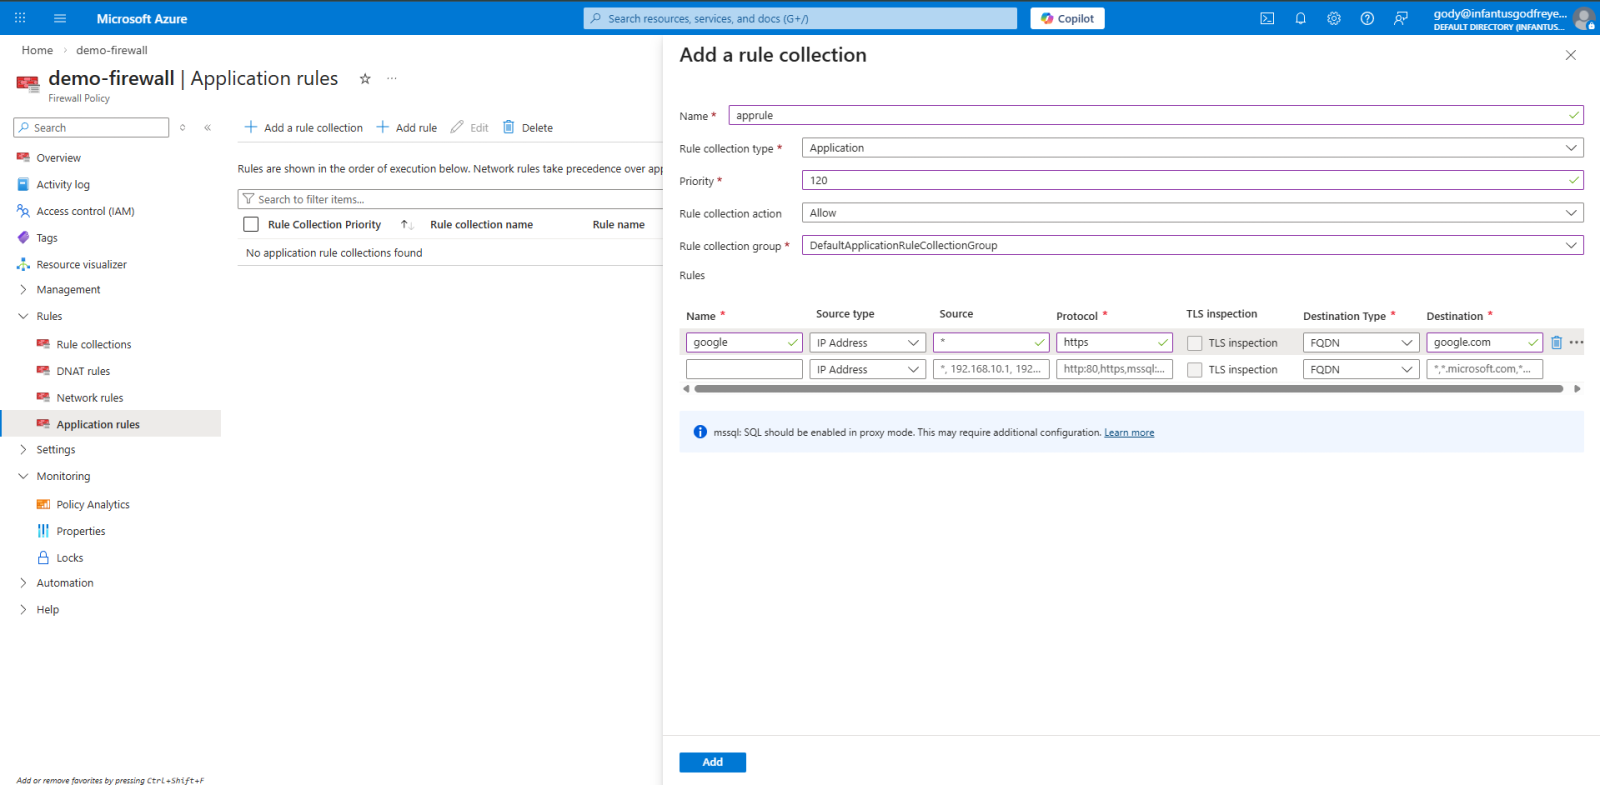
Step 13: Create an application rule
Firewall Policy → Application Rules → Add Rule Collection:
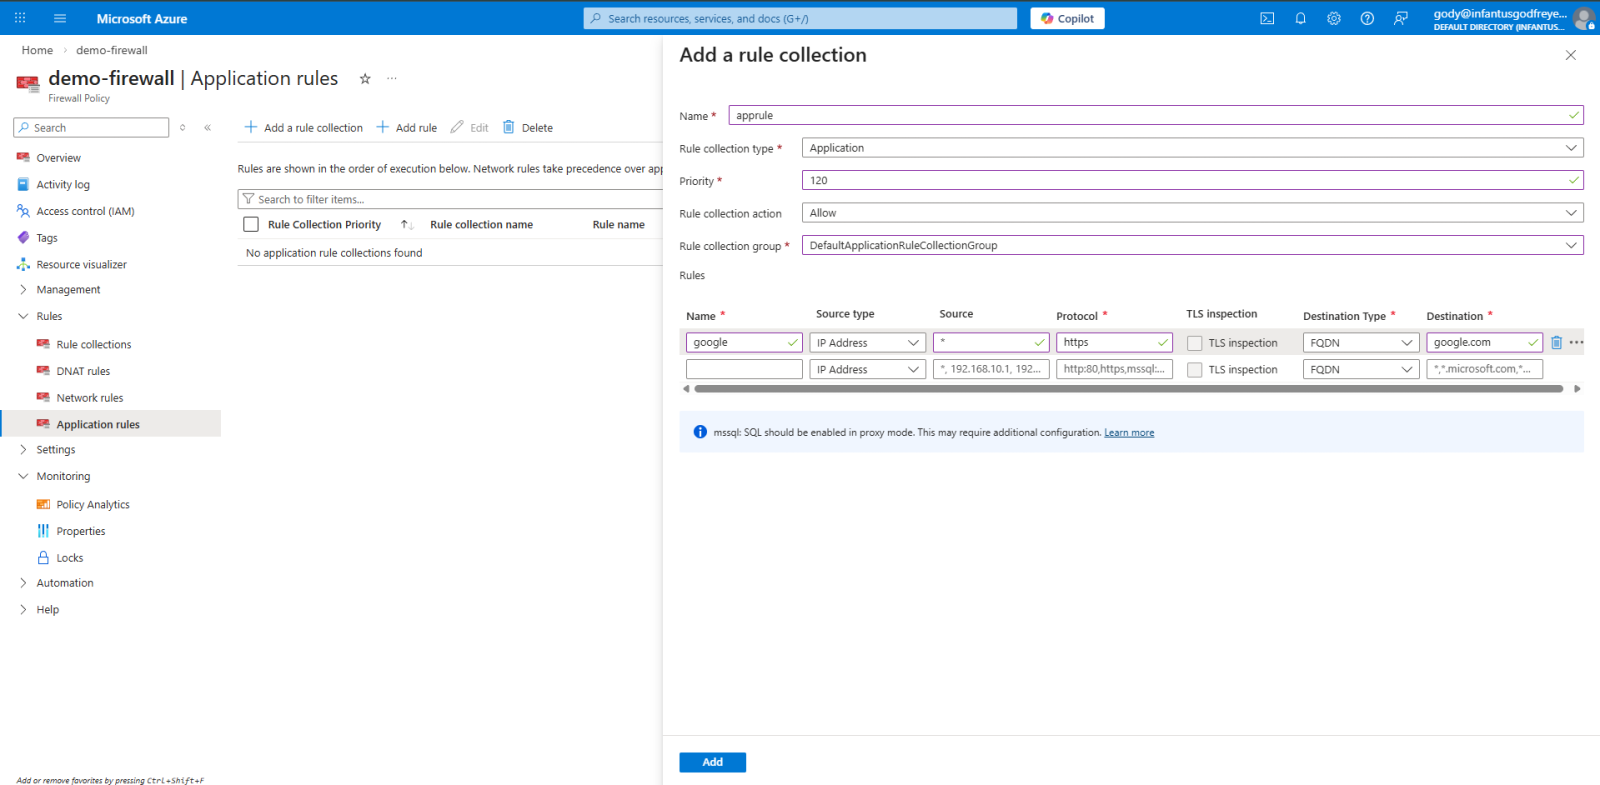
| Field | Value |
|---|---|
| Name | apprule |
| Type | Application |
| Priority | 120 |
| Action | Allow |
| Source | * (or 10.1.1.4) |
| Protocol | HTTPS |
| Destination Type | FQDN |
| Target FQDN | google.com |
Test again from the VM:
bash
curl https://www.google.comThis now returns the full HTML response, confirming:
- UDR is working
- The firewall is inspecting traffic
- The application rule is functioning
- Outbound HTTPS is allowed correctly
Why the network rule alone wasn't enough
Azure Firewall processes rules in this order: DNAT → Network Rules → Application Rules. But HTTPS filtering by FQDN only works through Application Rules.
When the network rule used Destination: *, Port: 443, the firewall allowed TCP 443 traffic but performed no FQDN filtering it had no way to know which HTTPS destination was being reached. The Application Rule uses Layer 7 inspection: it matches the FQDN, applies proper outbound handling, and enables secure web filtering. Network rules work on IP and port; HTTPS filtering by domain requires Layer 7, which only Application Rules provide.
Key architect-level learnings from this lab
- Always validate effective routes first - If traffic isn't reaching the firewall, rules don't matter.
- Network rules ≠ application rules - Network Rule = IP + port. Application Rule = FQDN + Layer 7.
- HTTPS needs an application rule - especially for FQDN filtering.
- Ping success doesn't guarantee HTTPS success - ICMP and HTTPS are inspected differently.
- Rule priority matters - lower number means higher precedence.
Troubleshooting checklist (from this lab)
If curl fails:
- Check Effective Routes
- Check NSG outbound rules
- Check that the Application Rule exists
- Check rule priority
- Check Firewall logs
- Verify DNS resolution
- Confirm peering settings
This lab moved beyond basic firewall deployment into real-world operational validation not just standing up Azure Firewall, but proving traffic actually flows through it correctly, and diagnosing it when it doesn't.
What we built and verified
- Forced all outbound traffic through Azure Firewall via UDR
- Validated routing using Effective Routes, before and after
- Implemented a Network Rule (Layer 3/4)
- Implemented an Application Rule (Layer 7, FQDN-based)
- Debugged an HTTPS failure that a network rule alone couldn't fix
- Verified real-time traffic inspection end to end
What we learned
- Routing is foundational a firewall without correct UDR in place does nothing
- Network rules alone aren't sufficient for modern HTTPS traffic
- Application rules are mandatory for FQDN-based filtering
- Testing with
pingandcurlgives clear, distinct validation signals for different layers
This mirrors a pattern common in production environments: "ping works but HTTPS fails." Understanding the difference between L3/L4 and L7 inspection is what separates a cloud engineer who can deploy a firewall from one who can actually operate and troubleshoot it.
Azure Firewall is not just a routing appliance it's a security control plane.
Real-world production best practices
- Use Firewall Policy, not classic rules
- Separate rule collection groups by purpose
- Use FQDN tags for known Azure services rather than hand-listing domains
- Enable diagnostic logs and send them to Log Analytics
- Avoid
Destination: *in production scope sources and destinations tightly - Use Private DNS where needed
- Document the purpose of every rule
Recommended next steps
| Priority | Recommendation | Benefit |
|---|---|---|
| High | Replace Source: * rules with scoped IPs/ranges | Removes an overly broad rule that was only used for lab testing |
| High | Send Firewall diagnostic logs to Log Analytics | Gives you a queryable audit trail instead of relying on the portal view |
| Medium | Add FQDN tags for known Azure service dependencies | Avoids manually maintaining long allow-lists |
| Medium | Evaluate Premium SKU if TLS inspection or IDPS becomes a requirement | Unlocks east-west TLS inspection and signature-based threat detection |
| Medium | Extend the hub-and-spoke pattern to additional spokes | Centralizes policy across more than one workload VNet |
| Low | Build a workbook combining Firewall logs and rule-hit metrics | One dashboard for ongoing policy review |
That was the first lab, free
Sign in (free) to mark this lab complete, earn your first 50 XP and start a streak.
You just ran the full first lab end to end. The rest of the bundle unlocks when you enrol once - and every lab you finish earns XP and counts toward your ByteLabs certificate.
Get "Azure Operations Labs" · ₹767