
Linux Networking Commands Every Cloud Engineer Needs
What you build: ip, ss, dig, curl, tcpdump and nc on real traffic on a free VM, plus three real breaks: a wrong listen address, a VPC firewall and a bad /etc/hosts line.

✍️ Translate this blog into Hindi, Tamil or Telugu
"The app works on the server but nobody can reach it" is one of the most common tickets a cloud engineer gets. In this lab you learn the Linux commands that answer it: ip, ss, dig, curl, tcpdump, ping and nc. You run each one on real traffic on a free Google Cloud VM, then you break the network three ways (an app listening on the wrong address, a firewall that drops the port, a wrong line in /etc/hosts) and find each cause with these tools.
Who it is for: beginners who can use a Linux terminal and want to debug network problems instead of guessing. Time: about 1 hour. Cost: free. An e2-micro VM in us-east1 is in Google Cloud's Always Free tier (one per account), and we delete it at the end.
Every command below was run for real by the CareerByteCode Team on a fresh Google Cloud project, and every output and screenshot is the real result we got. Public IP addresses are hidden and shown as EXTERNAL_IP. Private addresses like 10.142.0.16 are only valid inside a project, so we show them.
Part A: networking in plain English
When a program on one computer talks to a program on another, five questions must all have the answer "yes":
- Does the name resolve? DNS turns
www.example.cominto an IP address (dig,getent). - Is there a route? The server knows where to send packets (
ip route,ping). - Does a firewall let it through? In Google Cloud the VPC firewall sits outside the VM.
- Is something listening on that port, on the right address? (
ss,nc). - Does the program answer correctly? (
curl).

Words you will use:
- IP address: the number of a machine on a network, like a house number. Private ones (
10.x.x.x) work inside your VPC, public ones on the internet. - Port: a door number on that machine. Web servers use 80 (HTTP) and 443 (HTTPS), SSH uses 22. Real-life example: the IP address is the building and the port is the flat number.
- Listening: a program waiting for visitors at a port. It listens on an address too:
127.0.0.1(only the machine itself) or0.0.0.0(every address the machine has). - TCP handshake: before any data, the two sides send SYN, SYN-ACK, ACK, like "Hello?", "Hello, I hear you", "Great, let's talk".
- DNS: the internet's phone book.
/etc/hostsis your machine's own small phone book that it checks first.
Before you start
- A Google Cloud account (the free trial works) and a project.
- Open Cloud Shell (the
>_icon at the top right of the Google Cloud console) and set your project:
export PROJECT_ID="your-project-id"
gcloud config set project $PROJECT_ID
gcloud services enable compute.googleapis.com
Part B: the lab
Step 1: a free e2-micro VM
Why: a small Linux server (Debian 12) with a private and a public address. --no-service-account --no-scopes gives it no Google Cloud permissions; this lab needs none.
gcloud compute instances create net-lab --zone=us-east1-b --machine-type=e2-micro \
  --image-family=debian-12 --image-project=debian-cloud --boot-disk-size=10GB --boot-disk-type=pd-standard \
  --no-service-account --no-scopes 2>&1 | tail -2
until gcloud compute ssh net-lab --zone=us-east1-b --tunnel-through-iap --command="echo ssh ok" 2>/dev/null | grep -q ok; do sleep 10; done; echo "SSH works"
NAME ZONE MACHINE_TYPE PREEMPTIBLE INTERNAL_IP EXTERNAL_IP STATUS
net-lab us-east1-b e2-micro 10.142.0.16 EXTERNAL_IP RUNNING
SSH worksConnect with Compute Engine > VM instances > SSH next to net-lab, or from Cloud Shell gcloud compute ssh net-lab --zone=us-east1-b. Steps 2 to 9 and 12 to 14 run inside the VM in a folder ~/lab267. Steps 10 and 11 run in Cloud Shell, outside the VM, like a real visitor.
Step 2: install the tools
Why: Debian already has ip, ss, ping and curl. dnsutils gives dig, tcpdump captures packets, netcat-openbsd gives nc, and nginx is a web server so we have real traffic to look at. -qq keeps apt quiet.
# Install the tools (Debian has ip, ss and curl already; dig, tcpdump and nc come in small packages)
sudo apt-get update -qq && sudo DEBIAN_FRONTEND=noninteractive apt-get install -y -qq dnsutils tcpdump nginx netcat-openbsd > /dev/null
dig -v 2>&1 | head -1; tcpdump --version 2>&1 | head -1; curl --version | head -1 | cut -d' ' -f1-2; /usr/sbin/nginx -v 2>&1
DiG 9.18.49-1~deb12u3-Debian
tcpdump version 4.99.3
curl 7.88.1
nginx version: nginx/1.22.1Step 3: addresses, routes and the DNS server (ip)
Why: ip -br addr (brief) lists each network card and its addresses. ip route shows where packets go. /etc/resolv.conf names the DNS server the machine asks.
# Who am I on the network? Addresses, routes and the DNS server
ip -br addr
ip route
grep -v "^#" /etc/resolv.conf | grep .
lo UNKNOWN 127.0.0.1/8 ::1/128
ens4 UP 10.142.0.16/32 metric 100 fe80::4001:aff:fe8e:10/64
default via 10.142.0.1 dev ens4 proto dhcp src 10.142.0.16 metric 100
10.142.0.1 dev ens4 proto dhcp scope link src 10.142.0.16 metric 100
169.254.169.254 via 10.142.0.1 dev ens4 proto dhcp src 10.142.0.16 metric 100
nameserver 169.254.169.254
nameserver 169.254.169.254
search us-east1-b.c.your-project-id.internal c.your-project-id.internal google.internal
How to read it:
lois the loopback card (127.0.0.1, the machine talking to itself).ens4is the real card with the private address10.142.0.16.default via 10.142.0.1means "anything not local goes to the VPC gateway".nameserver 169.254.169.254is Google's metadata server, which answers DNS for every VM. Thesearchline lets you use short names likenet-labinside the project.- Notice that the public IP is not on the VM. Google Cloud translates it outside the VM, so
ip addrshows only the private one.
Step 4: which programs listen where (ss)
Why: ss -tulpn = TCP and UDP sockets, listening ones, with the process, as numbers. sudo is needed to see process names.
# Which programs listen on which ports? (ss = socket statistics)
sudo ss -tulpn | grep -E "Netid|LISTEN" | awk '{print $1, $2, $5, $7}' | column -t
Netid State Local Peer
tcp LISTEN 0.0.0.0:5355 users:(("systemd-resolve",pid=350,fd=12))
tcp LISTEN 127.0.0.54:53 users:(("systemd-resolve",pid=350,fd=21))
tcp LISTEN 127.0.0.53%lo:53 users:(("systemd-resolve",pid=350,fd=19))
tcp LISTEN 0.0.0.0:80 users:(("nginx",pid=1568,fd=5),("nginx",pid=1567,fd=5),("nginx",pid=1565,fd=5))
tcp LISTEN 127.0.0.1:25 users:(("exim4",pid=719,fd=4))
tcp LISTEN 0.0.0.0:22 users:(("sshd",pid=984,fd=3))
tcp LISTEN [::]:5355 users:(("systemd-resolve",pid=350,fd=14))
tcp LISTEN [::1]:25 users:(("exim4",pid=719,fd=5))
tcp LISTEN [::]:80 users:(("nginx",pid=1568,fd=6),("nginx",pid=1567,fd=6),("nginx",pid=1565,fd=6))
tcp LISTEN [::]:22 users:(("sshd",pid=984,fd=4))nginx listens on 0.0.0.0:80 (every address, IPv4) and [::]:80 (IPv6). sshd on 22. The mail program exim4 listens on 127.0.0.1:25 only, so nobody outside can reach it. That difference matters in Break it 1.
Step 5: DNS with dig
Why: dig asks DNS a question and shows the answer. +short prints only the addresses. +noall +answer +stats prints the answer and how long it took. getent hosts resolves a name the same way your programs do (including /etc/hosts).
# DNS: turn a name into an address
dig +short www.google.com A | head -2
dig www.careerbytecode.in A +noall +answer +stats | grep -E "IN|Query time|SERVER"
dig +short nosuchname-cbc-lab.example.com A; echo "empty answer = no such name"
getent hosts metadata.google.internal
EXTERNAL_IP
EXTERNAL_IP
www.careerbytecode.in. 14400 IN CNAME careerbytecode.in.
careerbytecode.in. 14400 IN A EXTERNAL_IP
;; Query time: 4 msec
;; SERVER: 169.254.169.254#53(169.254.169.254) (UDP)
empty answer = no such name
169.254.169.254 metadata.google.internal
www.careerbytecode.in is a CNAME (an alias) for careerbytecode.in, which has an A record (the address). 14400 is the TTL: how many seconds others may cache the answer. A name that does not exist returns nothing.
Step 6: talk HTTP with curl, and time it
Why: curl -I gets only the headers, -v shows the conversation (lines starting with > are sent, < received), and -w prints timings. When a site is slow, the timings tell you whether DNS, the connection, TLS or the server is the slow part.
# curl: talk HTTP like a browser, and time each part of the request
curl -sI localhost | head -4
curl -s -o /dev/null -w "dns %{time_namelookup}s  connect %{time_connect}s  tls %{time_appconnect}s  total %{time_total}s  code %{http_code}\n" https://www.google.com/
curl -sv localhost 2>&1 | grep -E "^\* (Connected|Trying)|^> GET|^< HTTP" | head -4
HTTP/1.1 200 OK
Server: nginx/1.22.1
Date: Wed, 18 Nov 2026 20:17:16 GMT
Content-Type: text/html
dns 0.005691s connect 0.008198s tls 0.064915s total 0.102578s code 200
* Connected to localhost (127.0.0.1) port 80 (#0)
> GET / HTTP/1.1
< HTTP/1.1 200 OKFor https://www.google.com/: DNS was done after 6 ms, the TCP connection after 8 ms, the TLS (HTTPS) setup after 65 ms and the whole answer after 103 ms. The times add up: each one is counted from the start.
Step 7: watch the packets with tcpdump
Why: tcpdump shows the real packets on a card. -i lo watches loopback, -nn prints numbers instead of names, -c 6 stops after 6 packets, and 'tcp port 80' is the filter. We start it in the background, make one request with curl, and read the capture.
# tcpdump: watch the real packets of one HTTP request (the TCP handshake)
sudo timeout 8 tcpdump -i lo -nn -c 6 'tcp port 80' 2> /dev/null > dump.txt &
sleep 2; curl -s -o /dev/null localhost; wait
cut -c17- dump.txt | sed -E 's/, (win|options|length).*//'
IP 127.0.0.1.52008 > 127.0.0.1.80: Flags [S], seq 2637723817
IP 127.0.0.1.80 > 127.0.0.1.52008: Flags [S.], seq 545041113, ack 2637723818
IP 127.0.0.1.52008 > 127.0.0.1.80: Flags [.], ack 1
IP 127.0.0.1.52008 > 127.0.0.1.80: Flags [P.], seq 1:74, ack 1
IP 127.0.0.1.80 > 127.0.0.1.52008: Flags [.], ack 74
IP 127.0.0.1.80 > 127.0.0.1.52008: Flags [P.], seq 1:854, ack 74
The flags tell the story: [S] SYN ("Hello?"), [S.] SYN-ACK ("Hello, I hear you"), [.] ACK ("Great"), then [P.] push: the 73 bytes of the HTTP request and the 853 bytes of the answer. If you ever see only [S] packets with no [S.] coming back, a firewall is dropping them.
Break it 1: an app that listens on 127.0.0.1
A new app (a tiny Python web server) is started on port 8080, but bound to 127.0.0.1. This happens all the time with development servers.
# Break it: an app that listens on 127.0.0.1 only, so other machines cannot reach it
mkdir -p www && echo "hello from port 8080" > www/index.html
sudo systemd-run --unit=web8080 --working-directory=$PWD/www python3 -m http.server 8080 --bind 127.0.0.1 > /dev/null 2>&1; sleep 2
MYIP=$(hostname -I | awk '{print $1}'); echo "my private IP: $MYIP"
curl -s localhost:8080
curl -s --max-time 3 $MYIP:8080; echo "curl exit $?"
sudo ss -tlnp | grep 8080 | awk '{print $4}'
my private IP: 10.142.0.16
hello from port 8080
curl exit 7
127.0.0.1:8080From the VM itself it works. Using the VM's own private IP, curl exit 7 means "connection refused": nothing listens on 10.142.0.16:8080. ss shows why: 127.0.0.1:8080. Only the machine itself can use that address.
Fix it: listen on 0.0.0.0
# Fix it: listen on 0.0.0.0 (all addresses)
sudo systemctl stop web8080
sudo systemd-run --unit=web8080 --working-directory=$PWD/www python3 -m http.server 8080 --bind 0.0.0.0 > /dev/null 2>&1; sleep 2
sudo ss -tlnp | grep 8080 | awk '{print $4}'
curl -s $(hostname -I | awk '{print $1}'):8080
0.0.0.0:8080
hello from port 8080
Break it 2: the VPC firewall drops port 8080
Now the app answers on every address. From Cloud Shell (outside the VM) we try its public address.
# Break it (from Cloud Shell): the app works inside, but the internet cannot reach it. The VPC firewall drops port 8080.
EXT=$(gcloud compute instances describe net-lab --zone=us-east1-b --format="value(networkInterfaces[0].accessConfigs[0].natIP)")
curl -s --max-time 8 http://$EXT:8080/; echo "curl exit $? (28 = timed out)"
curl exit 28 (28 = timed out)curl exit 28 = timed out. Not "refused": nobody even answered. That is the sign of a firewall dropping packets. A new project allows only SSH (22), RDP (3389) and ping from outside, so port 8080 is silently dropped before it reaches the VM.
Fix it: a firewall rule for your address only
Why: open the port only to who needs it. --source-ranges=$MY/32 is your own public address (exactly one address), and --target-tags=web8080 applies the rule only to VMs with that tag. Then we test and delete the rule at once.
# Fix it: allow port 8080 from YOUR address only, on VMs with the tag web8080
EXT=$(gcloud compute instances describe net-lab --zone=us-east1-b --format="value(networkInterfaces[0].accessConfigs[0].natIP)")
MY=$(curl -4 -s https://ifconfig.me)
gcloud compute firewall-rules create allow-8080-me --network=default --allow=tcp:8080 --source-ranges=$MY/32 --target-tags=web8080 --format="value(name)"
gcloud compute instances add-tags net-lab --zone=us-east1-b --tags=web8080
sleep 15; curl -s --max-time 8 http://$EXT:8080/
gcloud compute firewall-rules delete allow-8080-me --quiet 2>&1 | tail -1
Creating firewall...
..Created [https://www.googleapis.com/compute/v1/projects/your-project-id/global/firewalls/allow-8080-me].
done.
allow-8080-me
Updated [https://www.googleapis.com/compute/v1/projects/your-project-id/zones/us-east1-b/instances/net-lab].
hello from port 8080
Deleted [https://www.googleapis.com/compute/v1/projects/your-project-id/global/firewalls/allow-8080-me].
The same app, the same VM; only the firewall changed. In the console this is VPC network > Firewall. Never open a port to 0.0.0.0/0 (the whole internet) unless it is a public web site.
Break it 3: a wrong line in /etc/hosts
/etc/hosts wins over DNS. One wrong line, often left over from a test, sends a name to the wrong place.
# Break it: a wrong line in /etc/hosts sends a name to the wrong place
echo "10.9.9.9 www.example.com" | sudo tee -a /etc/hosts
getent hosts www.example.com
curl -s --max-time 4 -o /dev/null http://www.example.com/; echo "curl exit $? (28 = timed out)"
dig +short www.example.com A | head -1 | sed 's/.*/dig asks DNS directly and gets a real address/'
10.9.9.9 www.example.com
EXTERNAL_IP www.example.com
EXTERNAL_IP www.example.com
curl exit 28 (28 = timed out)
dig asks DNS directly and gets a real addressgetent hosts (what programs use) now says 10.9.9.9, so curl times out trying to reach a machine that does not exist. dig asks DNS directly, skips /etc/hosts, and gets the real answer. **When dig and getent disagree, check /etc/hosts.**
Fix it: remove the line
# Fix it: remove the line; names resolve through DNS again
sudo sed -i '/www.example.com/d' /etc/hosts
getent hosts www.example.com > /dev/null && echo "resolves through DNS again"
curl -s -o /dev/null -w "code %{http_code}\n" http://www.example.com/
resolves through DNS again
code 200
Step 8: ping and nc
Why: ping checks that a host is alive and how far away it is (round-trip time). nc -zv checks if a TCP port is open without sending data. "succeeded" = something listens, "Connection refused" = the machine answered but nothing listens on that port.
# ping and nc: is a host alive, is a port open?
ping -c 3 -q www.google.com | tail -2
nc -zv -w 3 localhost 22 2>&1
nc -zv -w 3 localhost 3306 2>&1; echo "nc exit $?"
sudo systemctl stop web8080
3 packets transmitted, 3 received, 0% packet loss, time 2003ms
rtt min/avg/max/mdev = 0.441/0.607/0.920/0.221 ms
Connection to localhost (::1) 22 port [tcp/ssh] succeeded!
nc: connect to localhost (::1) port 3306 (tcp) failed: Connection refused
nc: connect to localhost (127.0.0.1) port 3306 (tcp) failed: Connection refused
nc exit 1Port 22 is open, port 3306 (MySQL) is refused because no database runs here. Compare the three answers you have now seen: connected (open), refused (no program on that port), timed out (a firewall drops it, or the address is wrong).
POC: prove it works
ip,ss,dig,curl -wandtcpdumpshowed the address, the listening ports, the DNS answer, the timings and the TCP handshake of a real request.- An app on
127.0.0.1refused the private IP; on0.0.0.0it answered. - The VPC firewall dropped port 8080 (exit 28); a rule for one address and one tag let it through.
- A wrong
/etc/hostsline broke a name whiledigstill worked; removing it brought back HTTP 200.
Quiz task: check what you learned
- curl says
Connection refused. Firewall or no listener? (Answer: no listener on that address and port. A firewall usually gives a timeout.) - Which command shows whether your app listens on 127.0.0.1 or 0.0.0.0? *(Answer:
sudo ss -tlnp.)* diggives the right address but your app connects somewhere else. Where do you look? *(Answer:/etc/hosts, withgetent hosts <name>.)*- Why does
ip addron a Google Cloud VM not show its public IP? (Answer: Google Cloud maps the public IP to the private one outside the VM.) - Which tcpdump flags mean the server never answered the handshake? *(Answer: only
[S]packets, no[S.]back.)*
Clean up (delete everything)
The firewall rule was already deleted in Step 11. Exit the VM (exit), then in Cloud Shell:
gcloud compute instances delete net-lab --zone=us-east1-b --quiet 2>&1 | tail -1
echo "net-lab VMs left: $(gcloud compute instances list --filter="name=net-lab" --format="value(name)" | wc -l)"
echo "net-lab disks left: $(gcloud compute disks list --filter="name~^net-lab" --format="value(name)" | wc -l)"
Deleted [https://www.googleapis.com/compute/v1/projects/your-project-id/zones/us-east1-b/instances/net-lab].
net-lab VMs left: 0
net-lab disks left: 0
FAQ
**Is netstat still used?** It still works where it is installed, but ss replaces it and is installed everywhere. ss -tulpn is the same as netstat -tulpn.
**Why use dig and not nslookup?** Both ask DNS. dig shows the full answer (record type, TTL, server, time), which is what you need for debugging.
Can I run tcpdump on a busy server? Yes, but always use a filter (port 80, host 10.0.0.5) and a count (-c 100), and write to a file with -w capture.pcap to open it later in Wireshark.
Why did curl to the public IP time out instead of being refused? The VPC firewall drops packets silently, so curl waits until its time limit. "Refused" comes from the machine itself.
**What is traceroute for?** It shows each hop (router) on the way to a host. Inside Google Cloud many hops do not answer it, so ping, curl and VPC Flow Logs are more useful there.
How do I check the firewall from the command line? gcloud compute firewall-rules list shows every rule, its source ranges, ports and target tags.
Troubleshooting
| You see | Why | Fix |
|---|---|---|
Connection refused (curl exit 7) | Nothing listens on that address and port | sudo ss -tlnp; start the app or bind to 0.0.0.0 |
timed out (curl exit 28) | A firewall drops it, or the address is wrong | Check VPC firewall rules and tags, check the IP |
Could not resolve host | DNS has no answer for that name | dig <name>, check the spelling and the DNS record |
dig and the app disagree | A line in /etc/hosts overrides DNS | getent hosts <name>, fix /etc/hosts |
Must be a CIDR address range creating a rule | You passed an IPv6 address or no /32 | Use curl -4 ifconfig.me and add /32 |
| tcpdump prints nothing | Wrong card or filter | ip -br addr for the card name; -i any to watch all |
What next
- New to the terminal? Start with Linux for Cloud Beginners: 50 Commands on a Free VM.
- Build networks and firewall rules on purpose: Google Cloud VPC for Beginners: Subnets, Routes and Firewalls.
- Put a real web server on port 80 and 443: Nginx for Beginners: Web Server, Reverse Proxy and HTTPS.
- More hands-on posts: ByteBlog. Practice in ByteLabs and see the courses.
Prepared by the CareerByteCode Team from our tested lab, with AI help for the write-up.
⭐ Keep learning with CareerByteCode
Hand-picked to go deeper on this topicGet CareerByteCode Team's next blog by email
One email a week when they publish. Add the weekly Best of ByteBlog too. No spam, unsubscribe with one click.
We email you once to confirm. By subscribing you agree to the privacy policy.
Related blogs
 CareerByteCode Team
Linux for Cloud Beginners: 50 Commands on a Free VM
What you build: a free e2-micro Linux VM where you practise 50 everyday commands for files, text, permissions, processes, network and packages, in your own Google Cloud account. Every step tested.
#beginners CareerByteCode Team
Cron Jobs and Log Rotation on Linux
What you build: a disk report job run by cron every minute with its log rotated by logrotate, on a free VM, plus 3 real mistakes: relative paths, the % sign and an insecure log folder.
#beginners CareerByteCode Team
Linux Users, Groups and sudo Explained
What you build: a shared Linux server for 3 people on a free VM: users, a developers group, a sudo rule that allows one job only, visudo catching a typo, the sudo log, and an account locked and remove
#beginners CareerByteCode Team
From Windows to Linux: A Gentle Start for Beginners
What you build: everyday Windows tasks (files, search, zip, Task Manager, services, apps, network, admin) done the Linux way on a free VM, plus the 3 classic surprises and their fixes.
Readers of this blog also read
 Srilakshmi TFreelancer
SRE in Practice | Day 8: Availability Calculations - The Maths of Nines
Convert percentages to minutes, combine components, and calculate availability from incidents. Six hands-on labs with verified expected results.
#aws Srilakshmi TFreelancer
SRE in Practice | Day 3: The SRE Mindset
Look beyond "Is the server up?" and ask whether the service works reliably for the people who depend on it. Concept, infrastructure example, and a hands-on lab.
 Madhumathy UFreelancer
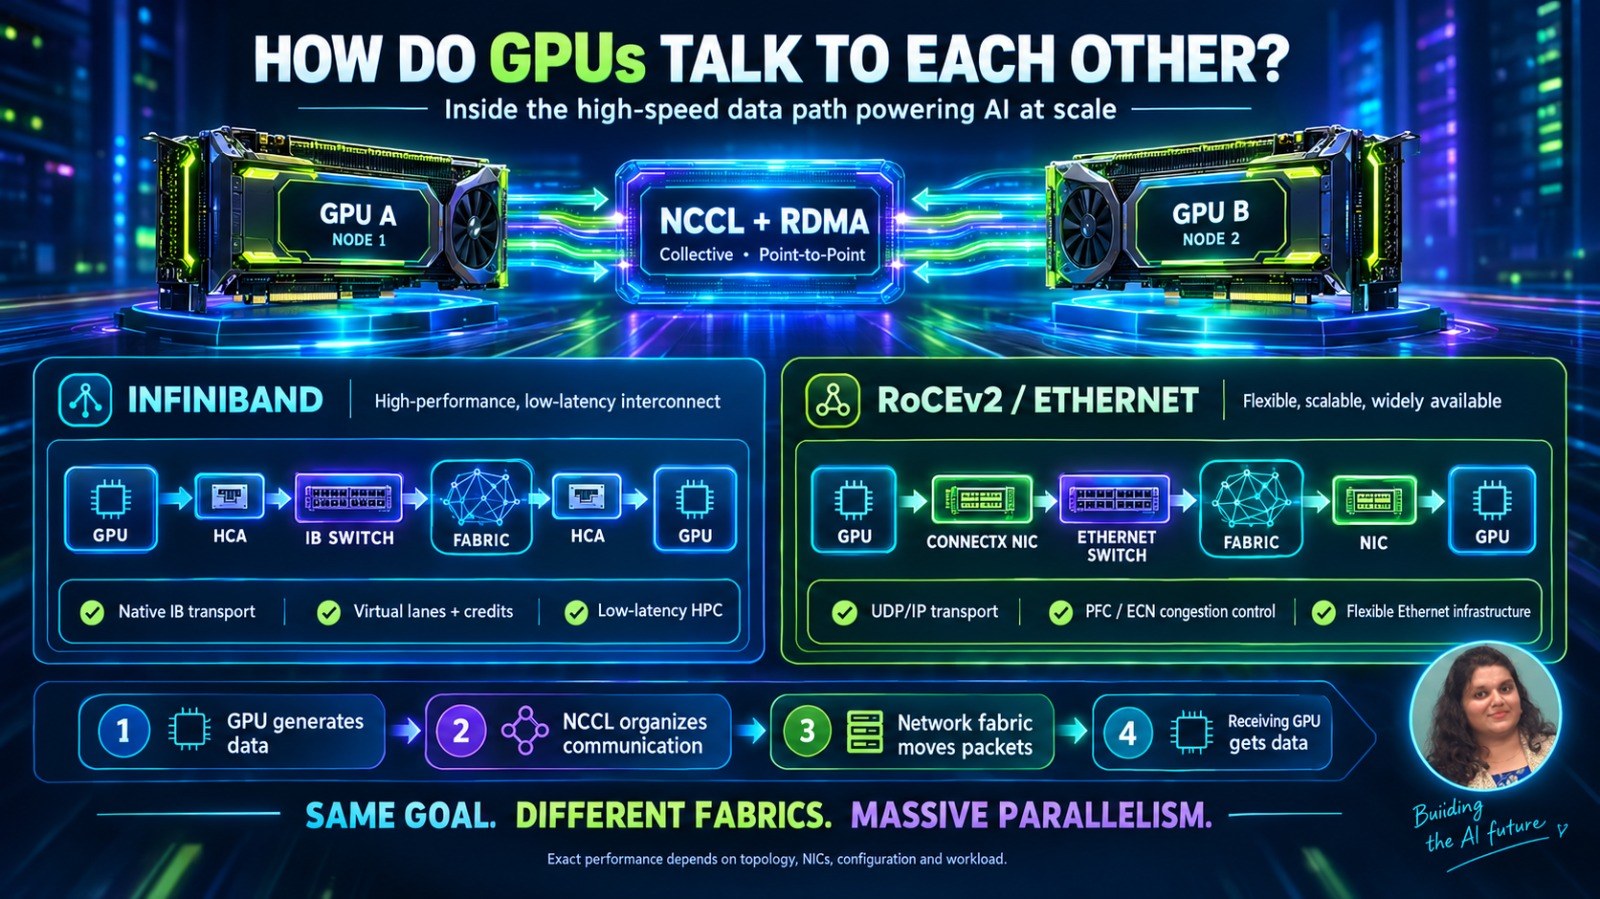
🚀 How Do GPUs Actually Talk to Each Other? The Hidden Network Powering AI at Scale
Your GPU may be incredibly powerful. But what happens when one GPU needs to communicate with hundreds of others?
#container
 Arun KumarFreelancer
Two Trucks: Explaining VMs and Containers
VMs and Containers
💬 Comments (0)
Top · NewestSign in to comment